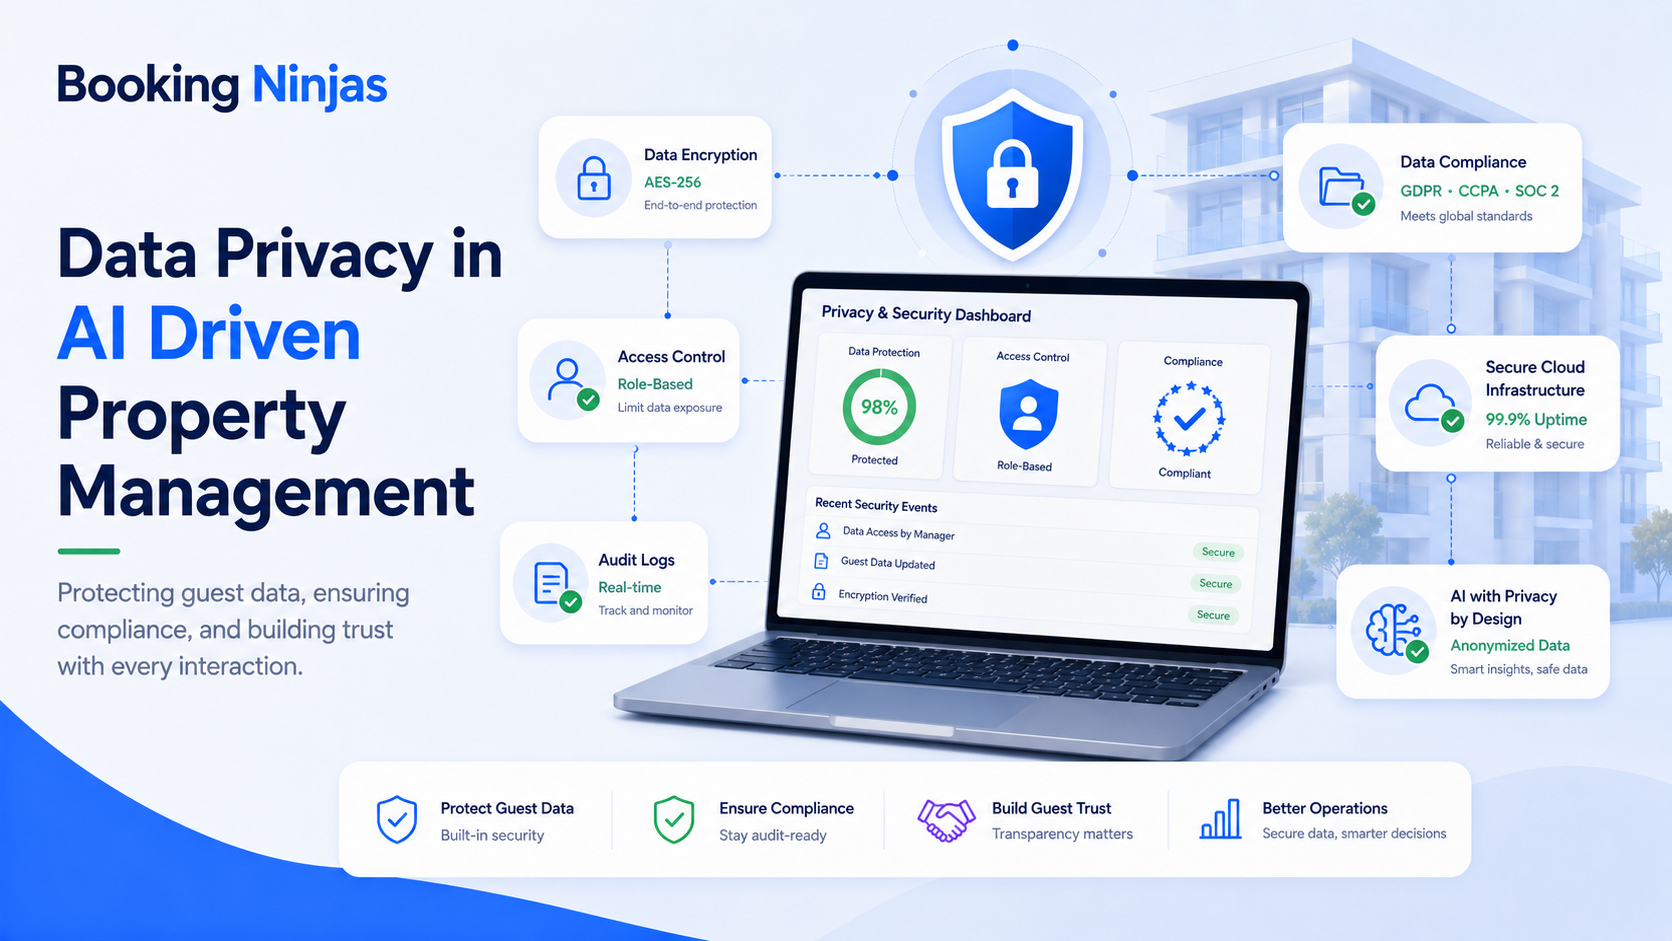
AI can summarize leases, classify service requests, analyze operational patterns, support forecasting, assist with communications, and contribute to other property workflows. The privacy question is not simply whether AI is being used. It is whether the organization controls which data enters the AI process, why it is used, who can access the result, and what decisions follow.
AI does not remove the organization's existing responsibilities for personal information. It can instead create additional questions because data may be summarized, classified, inferred from, combined, or transmitted to another service as part of the AI workflow.
What should property managers know about AI and data privacy?
- Not every property-management AI use case has the same privacy or decision-making risk.
- Collecting or retaining more data does not automatically make an AI system more appropriate.
- Access permissions should apply to AI workflows as well as the underlying property records.
- Consequential decisions require more governance than routine summarization or administrative assistance.
- External AI providers introduce additional data-flow and vendor questions.
- Privacy compliance depends on jurisdiction, data, purpose, workflow, and organizational responsibilities.
What does a privacy-aware AI workflow look like?
Identify the operational question and determine what data is genuinely required.
Apply the appropriate purpose, permissions, privacy rules, and integration boundaries.
AI analyzes or generates information within the approved operational context.
The result enters a controlled workflow with human review, logging, action, and retention rules where appropriate.
What property data can create privacy concerns when AI is introduced?
The answer depends on the property type and use case. AI workflows may potentially interact with information relating to people, transactions, spaces, communications, or behavior.
| Data area | Example | Privacy question |
|---|---|---|
| Identity and contact | Name, account information, contact details, identity-related records. | Does the AI use case actually require personally identifying information? |
| Applications and leases | Application information, documents, agreements, lease terms. | Is AI summarizing records or influencing an eligibility decision? |
| Financial activity | Invoices, payments, balances, payment history, financial documents. | Which financial fields are necessary for the defined analysis? |
| Service activity | Maintenance requests, communications, complaints, service history. | Could sensitive information appear inside free-text communications? |
| Access and usage | Access events, occupancy records, device events, portal activity. | Is the information necessary for operations, or is the organization creating unnecessary behavioral monitoring? |
| AI-generated inference | Classification, risk indicator, prediction, recommendation, or summary. | How reliable is the inference, and what action is allowed to follow it? |
What are the main privacy risks of AI in property management?
Collecting more data than the use case needs
An AI workflow should not automatically receive every field available in a tenant, resident, guest, applicant, owner, or customer record. The required input should follow the specific operational question.
Using information for a different purpose
Data gathered to complete one operational process should not be silently reused for unrelated profiling or decision-making without reviewing whether that secondary use is appropriate and permitted.
Giving AI broader access than the user should have
AI access should respect the underlying permission model. A user should not gain access to restricted records merely because an AI assistant can retrieve or summarize them.
Sending information to an unapproved external service
Generative AI can create a new data transfer when prompts or documents are sent to another provider. The organization should know what is transmitted, where it goes, what contractual terms apply, and how the provider handles the data.
Making consequential decisions from inaccurate outputs
AI can generate incorrect classifications, predictions, or summaries. The greater the impact on a person, the stronger the need for validation, documented criteria, and appropriate human review.
Keeping AI inputs and outputs indefinitely
Prompts, outputs, logs, derived data, and underlying records should follow defined retention requirements rather than remaining stored indefinitely simply because storage is available.

Are all property-management AI use cases equally sensitive?
No. Risk should be evaluated according to the data and the effect of the AI-supported process.
| Example use case | Primary concern | Governance approach |
|---|---|---|
| Summarizing maintenance history | Accuracy and unnecessary exposure of personal information. | Limit input fields, verify important facts, and control access to the summary. |
| Classifying a service request | Incorrect categorization or sensitive information in text. | Allow correction and escalation when classification is uncertain. |
| Drafting resident communication | Disclosure, incorrect content, or inappropriate personalization. | Restrict data access and review sensitive communications before sending. |
| Forecasting operational workload | Data quality and inaccurate predictions. | Treat output as planning support rather than certainty. |
| Tenant or applicant risk scoring | Housing access, discrimination, accuracy, explainability, and applicable screening laws. | Apply significantly stronger legal, data, testing, documentation, and human-review controls. |
| Biometric or behavioral monitoring | Sensitive data, surveillance, proportionality, consent or other legal requirements. | Conduct use-case-specific legal and privacy review before deployment. |
Why does AI-assisted tenant screening require special care?
Screening can directly affect whether someone receives housing or the conditions under which housing is offered. That makes accuracy, consistent criteria, transparency, review, and applicable housing and consumer-reporting requirements especially important.
Property managers should be particularly cautious about allowing AI to infer applicant risk from unrelated behavioral data or other information that was not collected for an appropriate screening purpose.
Where a consumer report is used in a U.S. tenant decision, Fair Credit Reporting Act requirements may apply, including requirements around permissible purpose and adverse action. Fair-housing obligations can also apply to screening criteria and outcomes.
Booking Ninjas' Tenant Screening provides structured screening records and workflows inside Salesforce. The organization's screening criteria, external data providers, legal obligations, review process, and final decisions still require appropriate governance.
When should a person review an AI-generated decision or recommendation?
Human review becomes more important as the consequence of the output increases.
Review should be considered when AI contributes to decisions involving:
- Housing eligibility
- Applicant screening
- Financial risk treatment
- Access restrictions
- Disputed charges
- Safety or security response
- Sensitive personal circumstances
- Other significant effects on an individual
Human review should be meaningful. The reviewer needs sufficient information and authority to question, correct, or reject the automated result rather than simply approving it by default.
Which privacy and AI rules can affect property management?
Requirements depend on jurisdiction, organization, property type, people affected, data being processed, and the purpose of the AI system. There is no single global property-management AI compliance checklist.
| Framework | Why it can matter | Property-management consideration |
|---|---|---|
| GDPR | Governs qualifying processing of personal data and includes rules relating to transparency, purpose, data minimization, security, individual rights, and certain automated decisions. | Establish the appropriate basis and purpose for processing, control the data used, assess higher-risk processing, and review automated decision-making obligations where applicable. |
| California CCPA / CPRA regulations | California privacy rules include consumer rights and, for covered businesses and uses, requirements addressing automated decision-making technology, risk assessment, and cybersecurity auditing. | Determine whether the organization, processing, and AI use case fall within the applicable requirements rather than assuming every AI workflow is treated identically. |
| Fair Credit Reporting Act | Consumer reports used for qualifying U.S. housing decisions create specific responsibilities for landlords, property managers, screening companies, and other parties. | Review permissible purpose, report accuracy, adverse-action requirements, and responsibilities involving screening vendors. |
| Fair housing requirements | Housing decisions remain subject to applicable anti-discrimination rules when algorithms or AI participate in the process. | Evaluate criteria, data sources, outcomes, and escalation processes rather than assuming a standardized algorithm is automatically neutral. |
| Other national, state, and local laws | Privacy, biometric, surveillance, consumer protection, housing, cybersecurity, and AI-specific requirements vary. | Review the actual jurisdictions and use cases involved in each deployment. |
This article provides an operational framework rather than legal advice. Organizations should confirm applicable requirements with qualified privacy, security, and legal professionals.
How should property managers design privacy into an AI workflow?
- Define the use case first. State the operational problem the AI system is meant to support and what output is expected.
- Map the required data. Identify the exact records and fields needed rather than giving the AI environment broad access by default.
- Establish the purpose and applicable privacy requirements. Determine why the data can be processed and what notices, permissions, consent, rights, or other controls apply.
- Map every external data flow. Document where information moves when external AI models, screening providers, data services, APIs, or integrations are involved.
- Apply role-based access. Restrict AI inputs, outputs, actions, and administrative controls according to the people who genuinely need them.
- Test the output. Check accuracy, failure modes, inappropriate inference, and the effect of incorrect AI results before allowing them into an operational workflow.
- Define where human review is required. Set explicit boundaries for consequential, ambiguous, sensitive, or exception-based decisions.
- Log important activity. Preserve appropriate records of inputs, outputs, approvals, changes, and decisions according to the use case and governance requirements.
- Define retention and deletion. Apply appropriate retention requirements to source data, AI outputs, logs, and derived information rather than inventing one universal retention period.
- Review the workflow after launch. Monitor incidents, user behavior, complaints, output quality, privacy requests, vendor changes, and changes in the applicable regulatory environment.
What should staff consider before putting property data into generative AI?
Generative AI makes it easy to copy a document, conversation, or record into a prompt. That convenience can bypass normal system boundaries if employees use unapproved tools.
Before property data is supplied to an AI service, the organization should understand:
- Which AI service is approved
- Which data categories can be submitted
- Whether unnecessary information can be removed
- How the external provider processes the data
- What retention terms apply
- Who can retrieve the output
- Whether human review is required
- How the resulting activity is documented
An integrated AI workflow is generally easier to govern than an informal process where employees individually copy operational data into unrelated consumer AI tools.
What should property managers ask an AI vendor about data privacy?
| Question | Why it matters |
|---|---|
| What data is transmitted? | Determines the actual exposure created by the integration. |
| Why is the data processed? | Helps identify use outside the organization's intended purpose. |
| Is customer data used to train or improve models? | Clarifies whether information may be reused beyond the immediate workflow. |
| How long are prompts, outputs, and logs retained? | Allows retention rules and contractual requirements to be evaluated. |
| Which subprocessors or infrastructure providers are involved? | Reveals additional parties in the data-processing chain. |
| How are access and authentication controlled? | Determines who can use the system and reach sensitive data. |
| What audit and logging information is available? | Supports investigation, accountability, and governance. |
| What happens when the integration fails or produces an incorrect result? | Establishes how the property operation handles exceptions safely. |
Certifications can be useful evidence during vendor review, but one certification should not replace a use-case-specific security, privacy, legal, and integration assessment.
How should privacy requests connect with property-management data?
Privacy governance becomes difficult when consent records, customer information, AI-derived data, and privacy requests are maintained in unrelated systems.
Depending on applicable requirements, organizations may need workflows around:
- Consent or preference records
- Access requests
- Correction requests
- Deletion requests
- Opt-out requests
- Processing restrictions
- Request verification
- Fulfillment history
Booking Ninjas' Data Privacy capabilities provide Salesforce-native consent records and structured privacy-request workflows. The exact rights and fulfillment process still depend on the law and organization involved.
Why should privacy controls be part of the operational workflow?
Privacy is easier to enforce when requirements become structured steps rather than policy documents employees must remember separately.
A workflow can require:
- Approval before a sensitive AI action
- Routing to an authorized reviewer
- Additional verification
- Human review of an AI recommendation
- Escalation of an exception
- Documentation of a decision
- Notification of responsible teams
- Completion of a privacy request
Booking Ninjas' Workflow & Process Management supports conditional routing, multi-step approvals, role assignments, escalation, exception handling, and tracked workflow execution.
How can Booking Ninjas support governed AI property workflows?
Booking Ninjas is a Salesforce-native platform for bookings and operations. AI can be connected with property, customer, operational, financial, and workflow data according to the configured implementation.
The important architectural advantage is that AI does not need to be treated as a completely separate operational environment. Relevant permissions, records, workflows, privacy processes, approvals, and audit context can remain connected within the Salesforce-based operating model.
This does not make every implementation automatically compliant. The organization remains responsible for defining appropriate AI uses, data access, user permissions, external vendors, integration scope, privacy requirements, human-review policies, and applicable legal obligations.
Connect predictive, analytical, and generative AI with property-management workflows and operational data.
Explore AI →Connect Salesforce AI and external AI services with defined property workflows, permissions, APIs, and operational records.
Explore AI Integration →Centralize consent records, privacy preferences, and structured data-subject request workflows.
Explore Data Privacy →Apply approvals, routing, escalation, exception handling, and human-review checkpoints to AI-supported processes.
Explore Workflow & Process Management →Maintain structured applicant, screening, approval, and review records where tenant screening is part of the operating model.
Explore Tenant Screening →Connect external systems through controlled API and middleware architecture according to the implementation scope.
Explore Integrations →Regulatory resources
Because privacy and automated-decision requirements change over time, property organizations should consult current authoritative sources for the jurisdictions and use cases relevant to them.
Frequently asked questions
What is the main data privacy risk of AI in property management?
There is no single risk for every AI system. Common concerns include unnecessary data collection, inappropriate secondary use, excessive access, external data transfers, inaccurate inferences, opaque decision-making, indefinite retention, and using AI output for consequential decisions without sufficient review.
Does using AI make a property management company automatically non-compliant with privacy laws?
No. Compliance depends on the specific use case, jurisdiction, data, purpose, legal responsibilities, technical design, vendors, notices, permissions, individual rights, and operational controls. AI introduces additional considerations but is not automatically prohibited.
Can AI make tenant screening decisions automatically?
Technical capability does not determine whether a fully automated screening decision is legally or operationally appropriate. Housing, consumer-reporting, privacy, discrimination, and automated-decision requirements may apply. Consequential screening workflows should therefore receive use-case-specific legal review and appropriate human oversight.
Should property managers send tenant data to public AI tools?
Property data should only be supplied to AI services that the organization has approved for the relevant use. Before sending personal or sensitive information, the organization should understand the service's data handling, retention, access, contractual, and security arrangements and remove unnecessary data where practical.
Does GDPR prohibit automated property-management decisions?
Not categorically. GDPR contains particular rules and safeguards for decisions based solely on automated processing that produce legal effects or similarly significantly affect a person. Whether those rules apply depends on the specific processing and circumstances.
Does California regulate automated decision-making technology?
Yes. California's privacy regulations include requirements concerning automated decision-making technology, including access and opt-out rights for covered uses, as well as risk-assessment and cybersecurity-audit requirements for certain businesses. Applicability depends on the organization and processing involved.
Does Booking Ninjas provide data privacy management capabilities?
Yes. Booking Ninjas Data Privacy provides Salesforce-native tools for consent records, privacy preferences, and structured data-subject request workflows. The organization remains responsible for configuring those processes according to its applicable requirements.
Is Booking Ninjas built on Salesforce?
Yes. Booking Ninjas is a Salesforce-native platform for bookings and operations. AI, privacy workflows, property records, permissions, automation, reporting, and integrations can therefore operate within the broader Salesforce-based environment according to the configured implementation.
Build AI around controlled property data
See how Booking Ninjas can connect AI, property records, permissions, privacy workflows, human review, integrations, and operational execution within a Salesforce-native environment.